COMPANY & LEADERSHIP
About RajSecure
RajSecure is an international cybersecurity consultancy focused on offensive security testing, vulnerability research, application security, cloud security, and actionable risk reduction.
RajSecure is the cybersecurity brand operated by RAJSECURENEXA CYVEXA PRIVATE LIMITED.
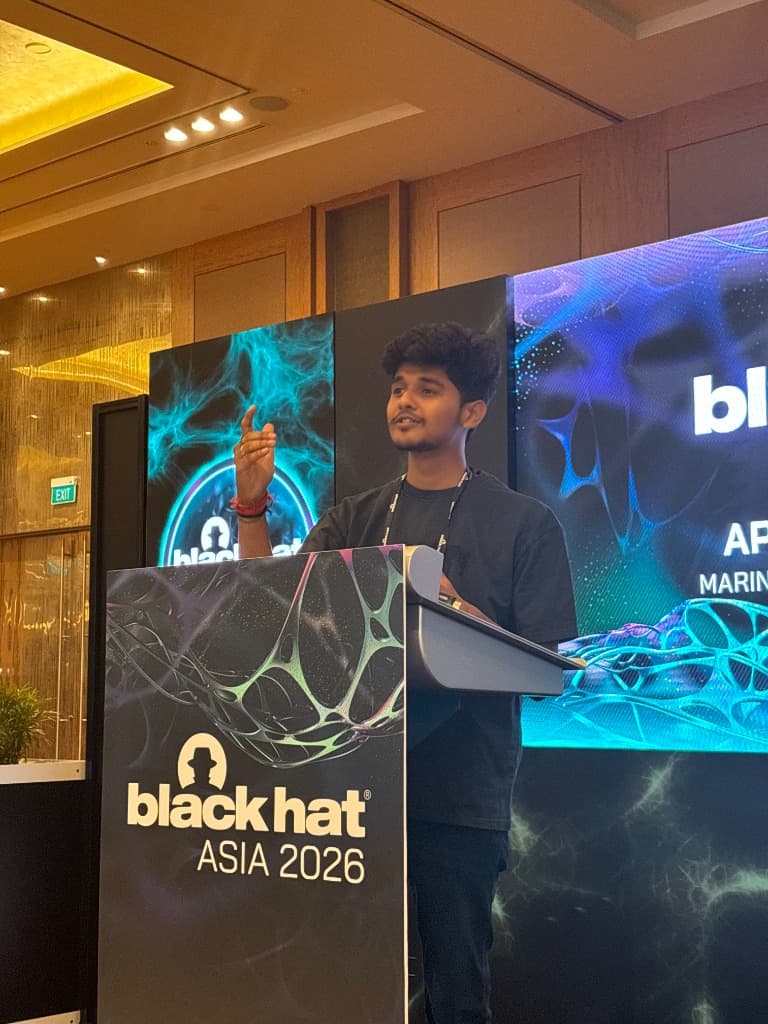
LEADERSHIP
Raj Kumar
Founder & CEO, RajSecure
Raj Kumar is the Founder & CEO of RajSecure. He leads the consultancy’s offensive security research, vulnerability assessment methodologies, and defensive engineering practices.
His approach combines practical attacker-informed threat modeling, responsible vulnerability testing, deep application-level analysis, and a relentless focus on delivering engineer-ready remediation that developers can execute immediately.
Industry Exposure & Continuous Learning
Black Hat Conference
Actively engages with the global cybersecurity research community and international industry events, including Black Hat, to integrate cutting-edge attack techniques and defensive standards into client engagements.
OUR ETHOS
Core Operating Principles
We believe in honest, evidence-backed security assessments that prioritize real-world exploitability over scanner noise.
Offensive Security Mindset
We approach your systems from an attacker perspective, finding deep business logic flaws and multi-step attack chains that automated scanners miss.
Evidence-Driven & Zero Noise
Every finding is backed by reproducible Proof of Concept (PoC) evidence and technical observation. No copy-pasted scanner dumps or false positives.
Business-Risk Prioritization
Vulnerabilities are evaluated by their tangible impact on data security, regulatory compliance, and business continuity — not generic scores.
Engineer-Ready Remediation
We deliver clear code-level remediation guidance, architectural recommendations, and direct developer debrief calls to accelerate fixes.
Strict Authorization & NDAs
All testing is strictly authorized under comprehensive non-disclosure agreements, defined boundaries, and secure encrypted data handling.
Verified Retesting Included
We don't just point out flaws; we verify your fixes through structured remediation retesting and provide executive Letters of Attestation.